CRM with API Integration for Government ICT Recruiters
Learn how CRM with API integration connects Australian Government ICT jobs, matches and evidence, plus the security and privacy rules to follow.
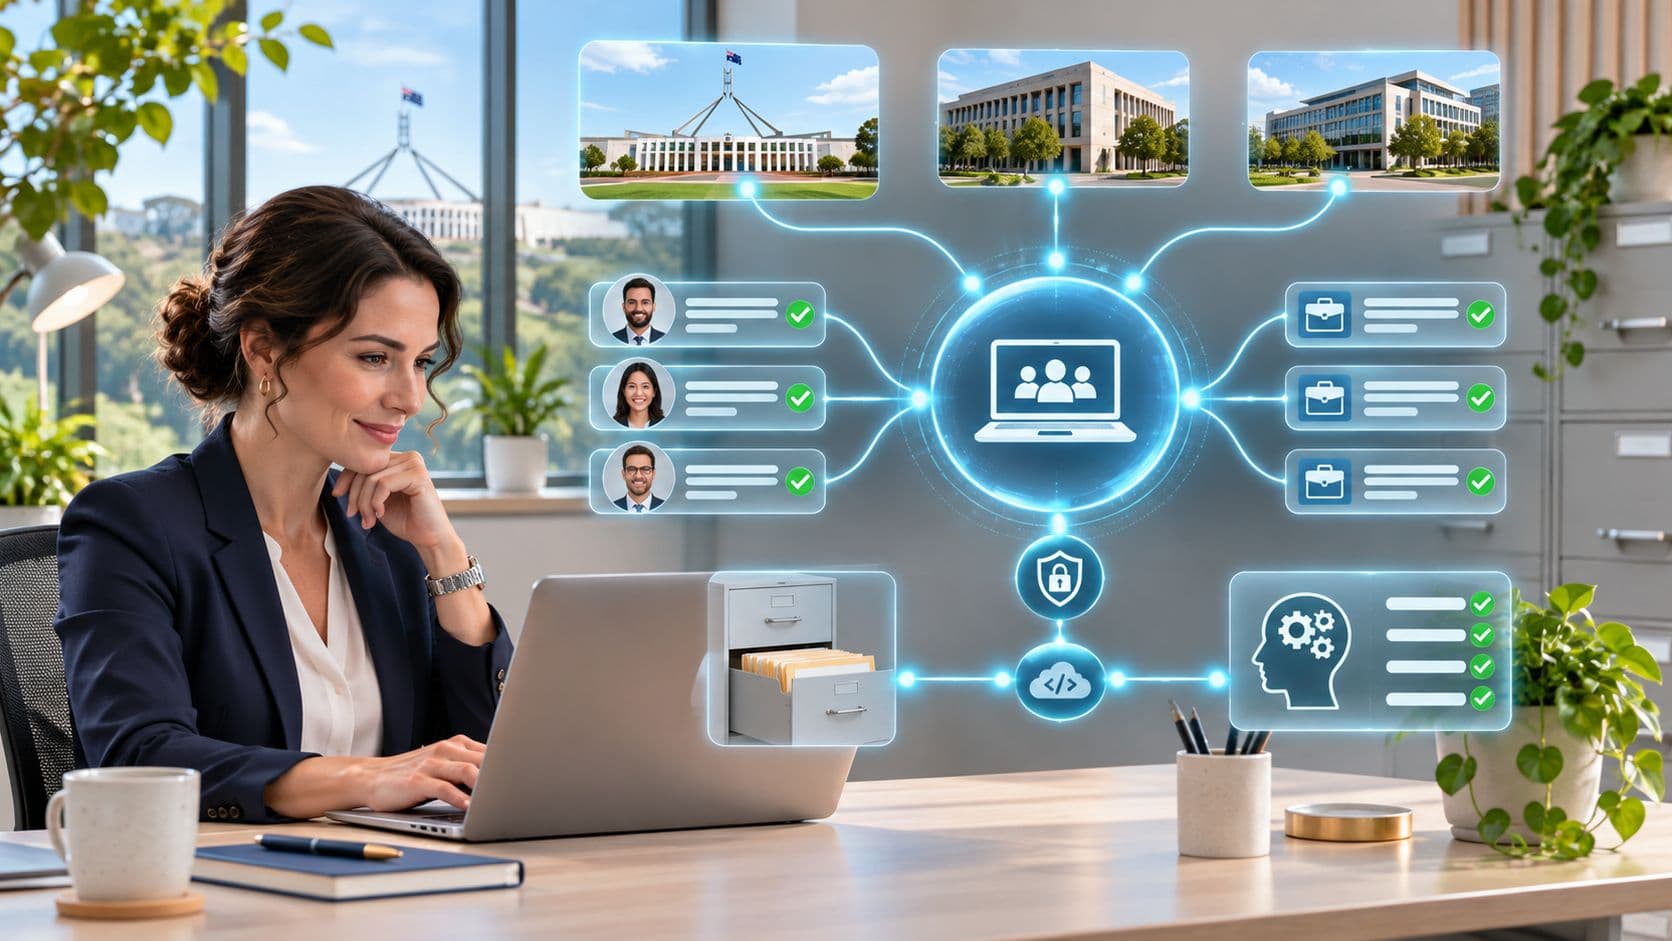
Most Australian businesses now run cloud systems, yet far fewer connect them to a proper CRM. The space between having cloud tools and having connected tools is where integration work lives. CRM, applicant-tracking, email and reporting environments rarely exchange data on their own.
For a recruiter working Australian Government ICT roles, the gap has a specific shape. The contract sits in BuyICT, the job ad sits on a tender-panel agency's career site, the CV sits in a workspace, and the clearance status sits in an email thread. Nothing joins those four things unless someone builds the join.
That join carries more responsibility than it first appears. A sync that moves a candidate name and a job title between systems has done very little. The version a recruiter can defend in front of an agency panel looks different: why the match exists, who approved it and when it was last checked. Those details have to survive the trip between systems intact, which makes every connection an evidence and audit problem before it is a connector problem.
Table of Contents
- What a CRM with API Integration Does for Government ICT Recruiters
- Minimum Evidence Fields Every Match Should Carry
- How Data Moves from Opportunity to CRM Record
- Troubleshooting Rate Limits, Missed Changes and Duplicates
- Securing API Access with Tokens and OAuth
- Consent and Privacy Rules for Candidate Records
- Keeping Reports Accurate When Opportunities Change
- Confirm the Integration Scope Before You Build
What a CRM with API Integration Does for Government ICT Recruiters
During 2023–24, 71% of Australian Government agencies reported critical shortages in digital and ICT skills, according to the Data and Digital Workforce profiles. The APS ICT and Digital Solutions job family held 7,556 ongoing employees at 30 June 2024, up from 6,757 one year earlier, and 845 ongoing employees were engaged into that job family during the year. A shortage that persists while headcount grows tells you the work is expanding faster than the people available to do it.
A CRM with API integration is two things joined. The CRM holds contacts, roles and pipeline stages. The API is the interface that lets other systems read and exchange that data automatically, rather than a recruiter copying a name from a job ad into a spreadsheet. In government ICT hiring, three sources feed the CRM:
- Opportunity data. A BuyICT request for a named role from a named agency, with notice text, closing date and any stated clearance.
- Candidate records. CV, extracted skills, clearance status and consent to be represented.
- Agency activity. Which tender-panel agencies are advertising which roles, and on which career sites.
Think of the CRM as the filing cabinet and the API as a courier that delivers a labelled copy of each file on a schedule. The courier matters less than the label. If the copy arrives without the contract ID, the clearance level or the date it was last seen, the recruiter ends up rebuilding that context by hand, which is the work the integration was meant to remove.
The cost of skipping the join is unglamorous and constant: double entry across a procurement notice and a CRM contact, candidate status that was accurate three weeks ago, and shortlists recorded with no trace of the contract behind them. Teams coming from other regulated sectors meet the same design question about consent and record provenance, and the CRM integration guide for healthtech teams works through how clinical records stay defensible through a sync. The logic transfers directly to candidate records.
Three questions follow from here. Which evidence must every synced match carry, how should access and consent be controlled, and how do you keep reporting honest when an opportunity changes after the first sync?
Minimum Evidence Fields Every Match Should Carry
Australian Government Architecture guidance states that APIs can improve productivity, efficiency, accuracy, visibility and management reporting, and its API standard requires government-facing APIs to apply the National API Design Standards, as set out in the API capability guidance. That's a strong mandate for the mechanism and almost nothing on the substance. Recruitment integration advice typically covers authentication, field mapping and contact synchronisation, then stops before the harder question: what context has to survive the trip so a recruiter can explain a shortlist six weeks later.
- Field — What it records — Why the CRM needs it
- Opportunity ID — The BuyICT opportunity the match relates to — Links the candidate to the actual contract, not a guess
- Panel supplier ad — Link and ID of the tender-panel agency job ad — Shows which panel supplier is advertising the role
- Clearance requirement — Baseline, NV1 or NV2 as stated on the notice, or flagged "not stated" — Screens candidates before submission
- Location and timing — Delivery location, working arrangement and closing date — Shows whether the candidate can realistically respond
- Match score and reasons — Confidence score with the skills and clearance behind it — Lets a reviewer challenge low-confidence matches
- Source timestamps — When the opportunity and ad were last seen — Shows whether the match is still current
- Change history — Each re-score, status change or closed date — Supports audit trails and reporting over time
Why the clearance field screens candidates before submission
Clearance isn't a nice-to-have tag. The AGSVA applicant guide sets out that Baseline covers classified resources up to and including PROTECTED, NV1 up to SECRET and NV2 up to TOP SECRET, and notes that a candidate can't apply independently because the sponsoring employer submits the request. Its published processing table lists 70 business days for NV1 and 100 business days for NV2. If that timing isn't visible on the record, a recruiter can shortlist someone who cannot possibly start when the agency needs them.
If the record can't answer why the candidate is there, it isn't evidence. It's an opinion with a timestamp.
The two rules that keep the evidence trustworthy
Use the source ID as the join key. Not the candidate's name, not the job title. Names repeat and titles get edited, so the source identifier is the only stable handle on a record.
Never overwrite evidence. Append an event. When a match is re-scored or a closing date moves, write a new change record with its own timestamp rather than editing the old value. The history is the audit trail, and an edited value destroys it.
Then route any low-confidence match to a named human reviewer before a candidate goes anywhere near a submission. The test of the whole schema is simple: a recruiter should be able to explain the match in one sentence using only the record in front of them.
How Data Moves from Opportunity to CRM Record
The mechanics are less mysterious than they sound. Six moves and one guardrail, in this order.
- Pull open opportunities, sorted by closing date. Page through every result within the provider's limit instead of taking the first response. The common slip is stopping at page one and missing the roles that close tomorrow.
- Pair each opportunity with the live job ad. A contract notice and a panel agency's advertisement are two different records describing one job. Store both IDs, or you'll never prove which supplier is hiring.
- Score candidates against the role. Keep the skills, clearance and score with the reasons attached, not just the number. Location belongs in that score as a filter rather than a preference, because the APS Digital Workforce Insights report records 58.3% of ICT and digital employees located in the Australian Capital Territory and 87% of 2023–24 APS ICT vacancies listing the ACT as an eligible location.
- Upsert with the source ID as the key. Upsert means update if the record exists and insert if it doesn't. Skip that and every run creates a fresh contact for a candidate you already have, which is how a database doubles in a month.
- Write the evidence fields in the same pass. Source timestamps, clearance, location, the panel ad link and the reasons behind the score all go in with the record, not in a later cleanup.
- Poll the list endpoints on a fixed schedule. An API without webhooks only shows you changes when you ask for them, so the schedule is part of the design, not an afterthought.
- Hold low-confidence matches for a reviewer. The guardrail sits between scoring and submission, and it's the step teams drop first when they're busy.
A healthy sync has two visible signatures. The record count from the source for a given date window matches the count in the CRM, and no source ID appears twice. When automating the recruitment workflow, build that comparison into the run rather than checking it after a complaint.
Troubleshooting Rate Limits, Missed Changes and Duplicates
Syncs rarely fail for exotic reasons. Five causes cover most of it, and each has a specific response.
- Rate limits. When the provider returns a throttling response, pause and retry with increasing delays. Re-running the whole window immediately is what turns a slow sync into a blocked one.
- Partial pages. If a run stops mid-pagination, resume from the last stored cursor and confirm the record count against the source before moving on.
- Missed changes. A webhook fails or a poll window gets skipped. Rerun the lost window using stored timestamps instead of trusting the last successful run to have caught everything.
- Duplicate records. Check whether the source ID exists before creating a contact, and merge rather than create when you find a match.
- Schema changes. When a field disappears from the published OpenAPI description, pause the mapping that depends on it and alert the owner before the next run.
Practical rule: log every failure with its correlation ID, so a reviewer can trace any record back to the request that produced it.
Integration failures get easier to reason about when you treat the pipeline as a set of independent connectors with their own retry behaviour, which is the framing in this Loopfour guide to SaaS software integration. One failing feed shouldn't stall the other four.
Securing API Access with Tokens and OAuth
Start with transport. Australian Government API security guidance requires HTTPS with at least TLS 1.2, per api.gov.au security requirements. Below that line, nothing is worth discussing.
Then match each control to the blast radius. erecruit's API is read-only and has no webhooks, and no endpoint returns CV text, so a leaked key cannot submit candidates or pull resume content. It can still expose opportunities, matches and agency activity, which is enough to reveal a desk's pipeline.
- Control — What it does — When to use it
- HTTPS with TLS 1.2 or higher — Encrypts data in transit — Every connection, without exception
- Bearer token — Authenticates the calling application with a key sent in the header — A single trusted service pulling read-only data
- OAuth 2.0 — Grants scoped, delegated access with short-lived tokens — Integrations acting for many users or workspaces
- Mutual TLS — Both sides present certificates before exchanging data — Higher-risk exchanges involving sensitive candidate data
- IP allowlisting — Accepts requests only from known addresses — Fixed server environments
- Payload signing — Shows that a message was not altered in transit — Inbound update traffic on systems that offer it
Operating rules for credentials
- One credential per agency tenant. Shared keys mean one compromised workspace exposes every client's pipeline.
- Restrict each credential to the scopes it needs. A connector that only reads opportunities has no reason to hold a write scope.
- Rotate short-lived tokens and log every access. Refresh-token rotation plus an audit log turns "who read this candidate record" into an answerable question when a shortlist is challenged.
- Keep tokens out of spreadsheets and chat threads. Use a secrets manager, and rotate immediately when someone leaves the team.
For a read-only pull into your own CRM and reporting, a bearer key sent in the Authorization header is usually sufficient, and the erecruit API documentation points to the OpenAPI 3.1 contract and the versioned /api/v1/ paths new integrations should use. A published schema, stable endpoints and correlation IDs make field mapping and failure recovery more predictable, because a reviewer can tie each synced record back to the request that produced it. For wider control options, browse practical API security controls covers the same ground from an engineering angle.
Consent and Privacy Rules for Candidate Records
A careless sync creates candidate profiles nobody agreed to and copies full CV text into every CRM user's view. The Australian Government CRM Standard addresses this directly. It recommends authenticating users before any information access, alteration or exchange, collecting only data required for a defined purpose, obtaining explicit and informed permission, and applying OAIC Australian Privacy Principles guidance. It also names API-based integration as a way to improve productivity, accuracy and visibility, which tells you the standard expects the connection to exist, just not to run unchecked.
The controls that make that work in practice are not complicated:
- Field-level allowlists. Synchronise only the fields a stated purpose requires. A pipeline stage rarely needs a date of birth.
- Consent status stored with purpose. Not a yes/no flag, but what the candidate agreed to and when.
- Immutable consent events. Approvals are appended with timestamps, so the history can be shown later rather than reconstructed.
- Representation approval before submission. No recorded approval, no submission to an agency.
- Deletion and correction flowing from the source. The system of record stays authoritative, and corrections propagate.
- Role-based access to CV text, with a retention period for cached copies.
What happens when a candidate withdraws consent
Say a candidate calls on Tuesday afternoon and withdraws consent to be represented for a particular agency. The withdrawal has to reach the CRM by the next polling cycle, change the consent state with a new event, and block any further submission from that record. If the only place that fact lives is a note in someone's inbox, the integration will keep proposing the candidate, and eventually someone will submit them. Data minimisation and consent decisions belong in the pipeline itself, not beside it.
Cross-border processing deserves the same scrutiny. api.gov.au frames interoperability and data security as connected modernisation challenges, and personal information can be processed overseas through middleware, logs, exports or downstream CRM users. That requires an assessment of Australian Privacy Principles obligations before go-live, not after a complaint. Local hosting alone doesn't solve it, because governance has to follow the data through every hop. The consent requirements for candidate representation set out what an approval record should contain before it counts.
Keeping Reports Accurate When Opportunities Change
The first sync is a snapshot. Opportunities then move: headcount gets revised, closing dates shift, notice text is corrected, a panel agency rewrites the ad. Each change may require re-scoring the candidates already matched against it.
When a re-score happens, record both the old and the new score alongside the reason. A score that changes from 82 to 61 with no explanation is worse than no score, because someone will eventually act on it.
Here's where instinct misleads teams. When an opportunity closes, the tidy move feels like deletion. Keep the record and mark it closed with a closed date instead. Win rates, time-to-submission and panel agency performance all depend on the closed record still existing, and a deleted row can't be reported on.
Deduplicate across the panel ad and the contract notice using source IDs as the join key, and never overwrite evidence. Add a change event.
Reconcile weekly: opportunities synced, matches created, time from match to submission, share of candidates with consent recorded, and low-confidence matches reviewed.
Compare those counts against the source each week and log any gap rather than adjusting the dashboard. For a visual walkthrough of how a pipeline is configured around these records, the video below is worth twenty minutes.
One last decision: which system is authoritative for each field. Keep the CRM as the place where recruiters act, decide the owner of every field before enabling two-way sync, and changes stop overwriting each other.
Confirm the Integration Scope Before You Build
Scope is the audit trail you build before the first record moves. Decide it while mistakes are still cheap, because a connector that syncs the wrong fields can look healthy right up until someone has to defend a shortlist.
- List the systems. CRM, applicant tracking, reporting tool. Decide where consent status, evidence fields and submission history will be stored. Forrester's State of Cloud in Australia and New Zealand report found 90% of Australian and New Zealand enterprises used multicloud strategies in 2024, as reported by ARN, so design for several environments.
- Choose the objects to sync. Opportunities, matches, agency activity and resume metadata such as id, filename, status, size, mime and date. CV text stays in the source, because the feed does not return it even to the uploading account.
- Decide if read-only is enough. erecruit's API cannot create or change records and has no CV upload endpoint. Plan submissions, stage changes and consent updates inside the CRM workflow.
- Set expectations for polling and pages. There are no webhooks, so schedule polls of the list endpoints. Only limit and offset are supported, limit defaults to 50, must sit between 1 and 200, and an out-of-range value returns a 400.
- Assign owners. One person owns consent records, and one named reviewer approves each low-confidence match before it reaches a client-facing list.
- Test in staging over a short date window. Confirm that evidence still travels with each match: role, clearance, location, timing and the link behind the ad.
On an Agency plan, erecruit's API pulls opportunities, matches and agency activity into your own CRM and tooling using a dashboard-issued bearer key and the OpenAPI 3.1 document at `/openapi.yaml`. Keep service content inside permitted use too: no scraping, mirroring or bulk redistribution without permission.
Go or no-go: every evidence field is mapped, consent status and purpose are stored, bearer keys are created in the dashboard and held per environment, polling and pagination are tested, reconciliation is scheduled, and a named reviewer exists. Miss any one and you are not ready.
The next step is small and concrete. Run the staging test this week over a seven-day window and log the first reconciliation result against the source.
erecruit maps every open BuyICT opportunity to the live job ad a tender-panel agency is running, and attaches the role, clearance, location and timing evidence to each match so your shortlists can be defended. Review the live feed of open and recently closed opportunities, check which panel agencies are advertising, and score a CV against the role before you commit to a build. When you are ready to connect your own systems, erecruit publishes the API documentation and OpenAPI description so you can see exactly which fields you can pull.